••
PHP vulnerability forces UK and European government websites offline
•2 min read•1 source
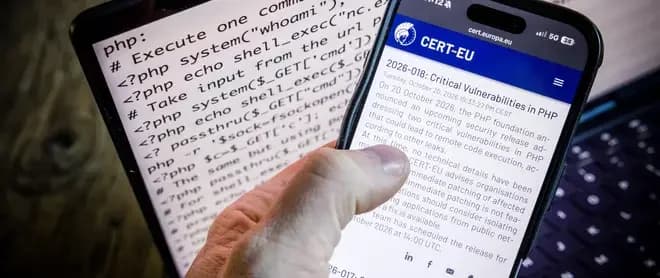
A critical security vulnerability in the PHP programming language has triggered widespread outages and service suspensions across the United Kingdom and Europe. The flaw has forced several government entities, police services, and major commercial platforms to take their websites offline to prevent potential exploitation by hackers. The National Cyber Security Centre (NCSC) in the UK has issued an urgent advisory to organizations, warning them to prepare for emergency updates or temporarily disable systems to maintain security.
The impact of the vulnerability has been felt across a broad range of sectors. In the UK, the official websites for the Metropolitan Police, as well as Edinburgh and Oxford City Councils, have experienced significant downtime. Major digital platforms, including Google Drive, WordPress, and the gaming service Steam, were also reported to have faced disruptions. The NCSC has emphasized that while full details of the vulnerability remain confidential to prevent further risk, the potential for unauthorized access by malicious actors is high.
The crisis has extended beyond British borders, prompting swift action from European governments. Finland has suspended its primary government web services as a precautionary measure, while the Netherlands’ national cyber agency chose to take its own website offline. These actions reflect the severity of the PHP flaw, which serves as a foundational component for a vast portion of the internet’s infrastructure. Owners of affected websites are being told they may need to keep services suspended until robust protective measures are fully implemented.
As technical teams work to patch the vulnerability, the NCSC is advising all organizations that utilize PHP to stay vigilant. The agency recommends that if immediate security fixes cannot be applied, the safest course of action is to take vulnerable systems offline entirely. This proactive approach aims to mitigate the risk of data breaches and system hijacks while developers release the necessary software updates to address the underlying code flaws.

