••
Hackers post false nuclear alerts on Russian and Ukrainian emergency apps
•2 min read•1 source
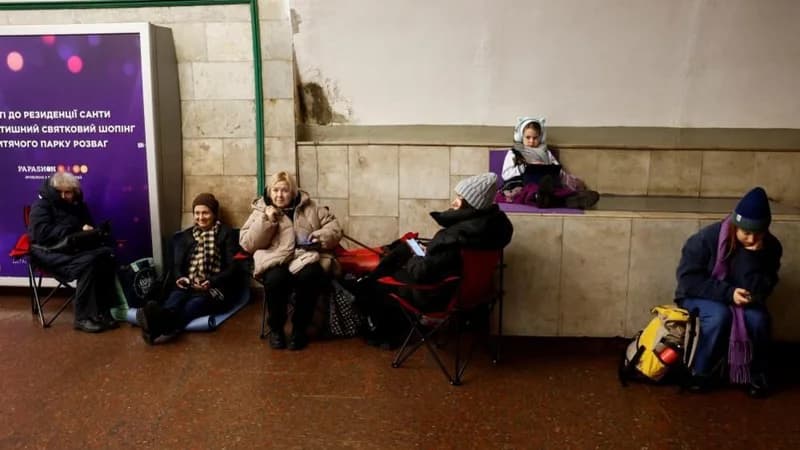
Unidentified hackers targeted emergency warning applications in both Russia and Ukraine, broadcasting false alerts concerning imminent nuclear strikes and chemical hazards. These digital platforms, which serve as critical components of public safety infrastructure in the conflict-hit region, were compromised to spread misinformation, triggering immediate responses from state authorities to clarify the situation and secure the systems. The breach occurred as both nations continue to rely heavily on digital communication for civilian defense and emergency coordination.
The unauthorized alerts caused immediate concern as mobile users received notifications regarding catastrophic threats. However, instead of the intended chaos, the public reaction was notably skeptical. Authorities in both countries were forced to issue rapid reassurances to the public, confirming that no such nuclear or chemical threats existed and that the notifications were the result of a coordinated cyberattack. Observers noted that in many online communities, the false alarms were met with humor rather than panic, reflecting a public that has become increasingly wary of digital misinformation.
Technical teams are currently working to fully restore the integrity of the emergency services and investigate the specific vulnerabilities exploited by the hackers. This incident underscores the significant risks facing digital infrastructure during periods of heightened geopolitical tension, where essential public safety tools can be weaponized for psychological impact. As both Russia and Ukraine move to reinforce their cybersecurity protocols, the breach serves as a stark reminder of the persistent threats to critical communication channels and the ongoing evolution of hybrid warfare.