••
CSA and NITA order state agencies to patch PHP flaws within seven days
•2 min read•3 sources
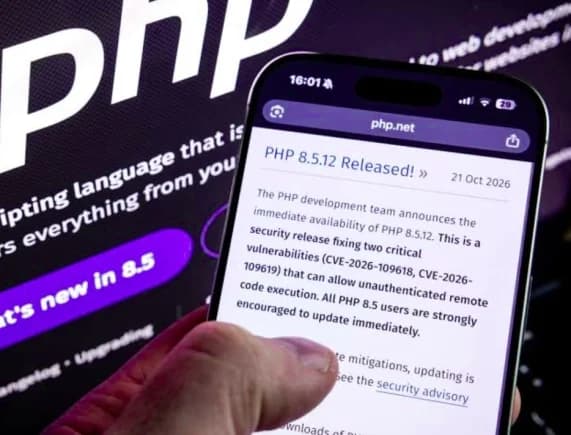
The Cyber Security Authority (CSA) and the National Information Technology Agency (NITA) have issued an urgent joint directive to all government institutions, mandating them to rectify critical security vulnerabilities in their PHP software within seven days. The alert, issued on October 22, 2026, warns that the flaws—specifically identified as CVE-2026-109618 and CVE-2026-109619—pose a severe risk to national digital infrastructure. Collectively referred to as "PHP2Shell," these vulnerabilities could allow unauthorized individuals to gain control of servers and sensitive data without requiring usernames or passwords.
The technical nature of these vulnerabilities means that attackers could bypass standard authentication protocols to access sensitive information or disrupt essential online services. According to the regulatory bodies, the PHP2Shell flaws are categorised as high-risk, potentially leading to complete server takeovers. Consequently, the CSA and NITA have provided a five-step remediation guide for technical teams across the public sector and private businesses to follow. The primary instruction is for organisations to update PHP installations to the most recent, secure versions immediately to mitigate the threat of external exploitation.
Beyond the technical fix, government agencies are required to coordinate their response directly with NITA and the CSA to ensure a unified defence against potential cyberattacks. The agencies emphasized that immediate reporting and coordination are mandatory for all state institutions to verify that their systems are properly secured. In addition to the directive for government bodies, the authorities issued a caution to the general public and private website operators. They warned against potential phishing scams and suspicious download requests that might masquerade as legitimate PHP updates, advising users to only source software patches from official and verified providers.
This swift regulatory action underscores the government's commitment to protecting Ghana’s digital ecosystem from evolving cyber threats. By setting a strict one-week deadline, the CSA and NITA aim to close security gaps before malicious actors can exploit them on a large scale. Organizations that fail to comply with the directive risk not only data breaches but also the potential loss of public trust and the disruption of critical digital services. The agencies have reiterated that they will continue to monitor the situation and provide further guidance as necessary to safeguard the country's information technology landscape.

